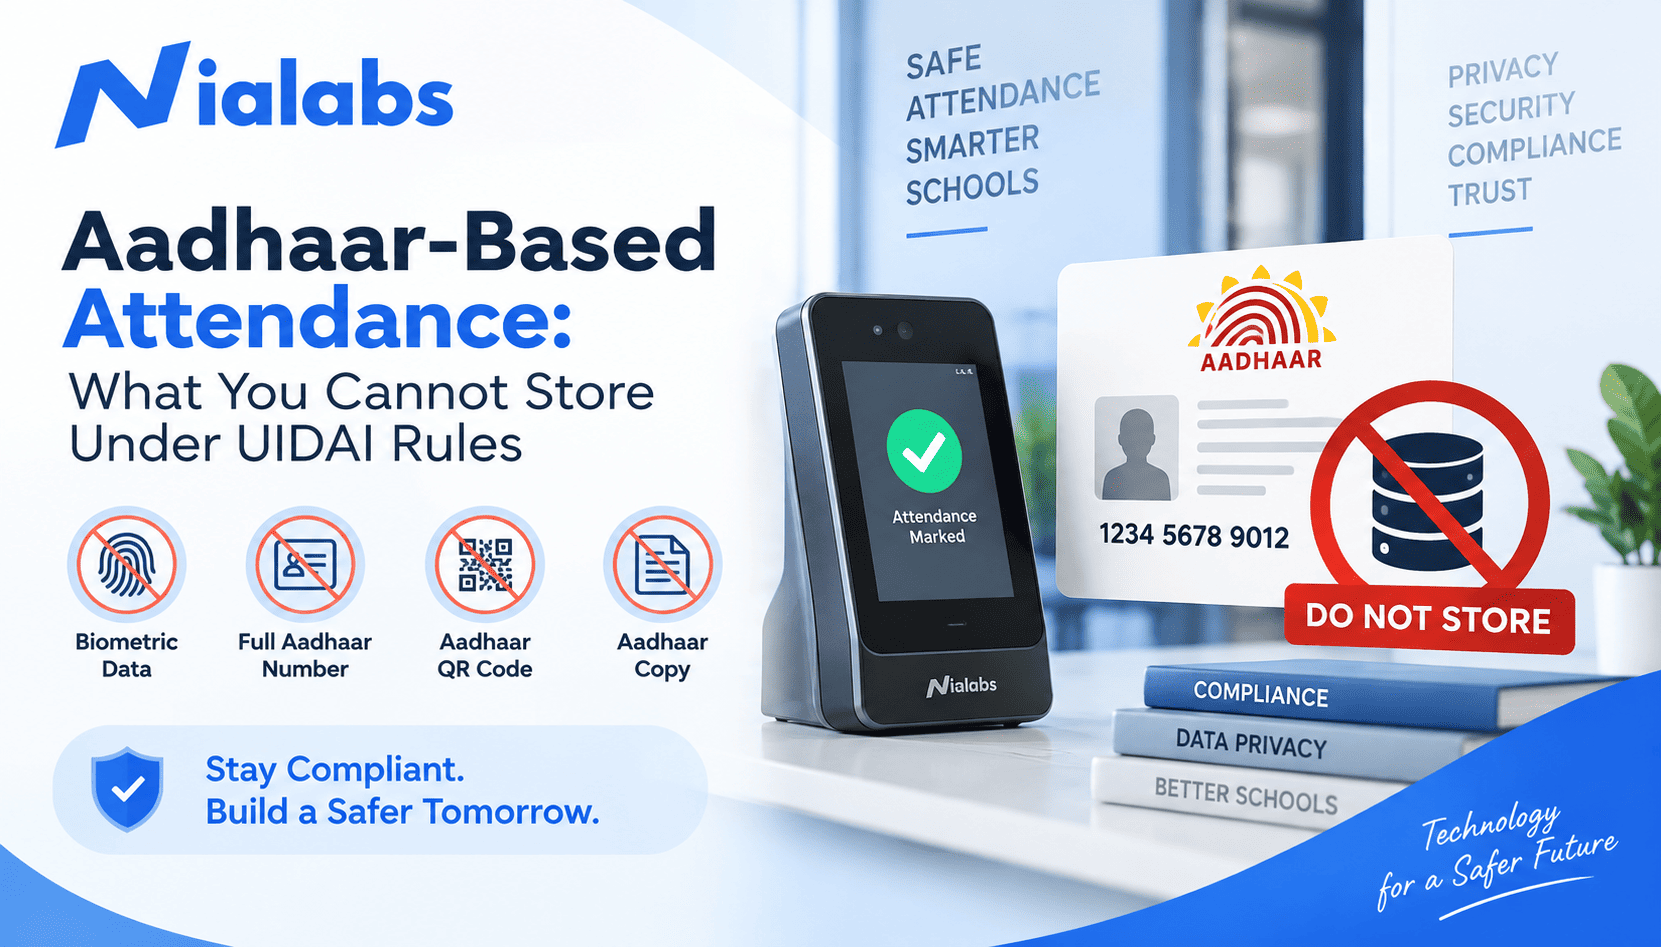
You cannot store fingerprints, iris data, OTPs, Virtual IDs, or encrypted PID blocks from Aadhaar authentication. Under UIDAI 2025 guidelines, organizations can only retain attendance records, employee/student IDs, names, timestamps, and department information. Storing sensitive authentication data violates UIDAI mandates and creates compliance liability for schools, hospitals, offices, and factories across India.
Aadhaar-based attendance systems offer streamlined identity verification and automated attendance marking. However, this convenience comes with strict legal obligations under the Aadhaar Act and UIDAI security protocols. Many organizations fail to distinguish between what can and cannot be stored, creating data security risks and compliance violations.
KEY TAKEAWAYS
Biometric data from Aadhaar authentication cannot be stored, copied, or retained by requesting organizations under any circumstances.
OTPs sent for Aadhaar authentication must not be stored permanently in attendance databases or employee records.
Virtual IDs (VIDs) are temporary and cannot be retained. Organizations must delete them after each authentication cycle.
Aadhaar numbers can only be stored in a dedicated Aadhaar Data Vault (ADV) as per UIDAI 2025 guidelines, not in general attendance systems.
Encrypted PID blocks can be cached for only 24 hours maximum before deletion. Retaining them as permanent records violates UIDAI mandates.
You can legally store attendance status (present/absent), timestamps, employee/student IDs, names, departments, and transaction references.
What is Aadhaar-Based Attendance?
Aadhaar-based attendance uses authentication methods authorised by UIDAI to verify identity and record attendance. The authentication can use biometric matching (fingerprint or iris), demographic data, OTP, or a combination of these methods.
When an employee or student authenticates using Aadhaar, the system verifies their identity through the UIDAI database and marks their attendance. The organisation receives confirmation of successful authentication but is not authorised to store the underlying authentication data itself.
This distinction is critical: the purpose of Aadhaar authentication is identity verification, not data collection. Organizations deploying Aadhaar attendance must design systems to log the attendance result while immediately discarding all sensitive authentication information.
What You Cannot Store From Aadhaar Authentication
|
Data Type |
Why It Cannot Be Stored |
|
Fingerprints or Iris Scans |
Core biometric data used for Aadhaar authentication is verified on UIDAI servers. Organizations cannot maintain copies or permanent records under UIDAI security protocols. |
|
OTP (One-Time Passwords) |
OTPs are temporary authentication codes with single use. Storing them violates UIDAI rules and creates security vulnerabilities. Must be discarded immediately after authentication. |
|
Virtual ID (VID) |
VIDs are temporary proxies for Aadhaar numbers, valid for a single transaction. They cannot be retained or reused. UIDAI mandates immediate deletion after use. |
|
Encrypted PID Block |
Personal Identity Data (PID) blocks can be cached for maximum 24 hours. Storing them as permanent records violates UIDAI guidelines. Encryption does not grant unconditional retention rights. |
|
Authentication Credentials |
API keys, authentication tokens, or session credentials used to verify identity with UIDAI cannot be stored in attendance databases or employee records. |
Aadhaar Biometric Data Storage Rules
The core restriction under UIDAI guidelines is absolute: organisations cannot store, copy, transmit, or maintain any record of fingerprints or iris data captured during Aadhaar authentication.
When a person authenticates using biometric data, their biometric template is compared to the UIDAI database. The comparison happens on UIDAI servers. Your organisation receives only a yes/no confirmation of the match. You do not receive the biometric data itself.
This is fundamentally different from a corporate biometric system, where fingerprints are enrolled locally and compared against an on-premises database. In Aadhaar authentication, the biometric never touches your servers.
OTP Data Storage and Compliance
OTPs sent for Aadhaar authentication are one-time-use codes. They expire after a few minutes and are rendered invalid after one use. Storing them serves no operational purpose and creates compliance violations.
UIDAI explicitly prohibits storing OTPs in permanent attendance databases, employee profiles, or any archive. Even if your system captures an OTP during authentication, it must be deleted immediately after verification.
Organizations often make this mistake: they log all incoming requests including OTPs for debugging or audit purposes. Audit logs containing OTPs must be purged regularly or excluded from permanent archives.
Virtual ID (VID) Storage and Limitations
Virtual IDs are temporary proxies for Aadhaar numbers, created to protect privacy during online transactions or e-KYC verification. A VID is valid for a single session or a limited time window, after which it expires.
Organizations cannot retain or reuse VIDs. You cannot store them in your attendance system as an alternative to Aadhaar numbers. This is a common compliance gap: teams assume VIDs are a workaround to avoid storing actual Aadhaar numbers, but UIDAI mandates apply equally to VIDs. After each authentication cycle, the VID must be deleted.
What About Storing Aadhaar Numbers Themselves?
Aadhaar numbers can be retained, but only under strict conditions defined in UIDAI 2025 guidelines. Organisations that retain Aadhaar numbers must create and maintain a dedicated Aadhaar Data Vault (ADV).
|
Requirement |
Compliance Detail |
|
Dedicated Data Vault (ADV) |
Aadhaar numbers must be stored in a separate, secure vault. Do not store them in your regular attendance database. |
|
Access Control |
Only authorized personnel handling Aadhaar authentication can access the ADV. No blanket access for HR or payroll teams. |
|
Encryption |
Aadhaar numbers in the vault must be encrypted using UIDAI-approved methods at rest and in transit. |
|
Retention Policy |
Aadhaar numbers must be deleted when no longer required for the specified purpose. |
|
Identifier Prohibition |
Do not use Aadhaar numbers as domain-specific IDs. They link to the ADV separately from main attendance systems. |
What You Can Legally Store in Your Attendance System
Your attendance system should focus on recording the attendance event, not the authentication data. The following data elements are compliant to store:
|
Data Element |
Example / Notes |
|
Employee or Student ID |
Your internal ID, not the Aadhaar number. Example: EMP-2024-0156 |
|
Name |
Full name as recorded in your HR or student information system |
|
Date and Time |
Attendance timestamp (e.g., 2026-09-19 08:45:23) |
|
Attendance Status |
Present, Absent, Late, Half-Day, Leave |
|
Department, Class, or Location |
Sales, IT, Class 12-A, Factory Gate-01 |
|
Transaction Reference |
Unique reference ID from UIDAI confirming authentication occurred without storing auth data. |
|
Audit Details |
System logs showing who made the entry and device used. No authentication data. |
Aadhaar Authentication vs. Regular Biometric Attendance
Understanding the difference between Aadhaar authentication and regular biometric attendance systems is critical for compliance.
|
Aspect |
Aadhaar Authentication |
Regular Biometric System |
|
Biometric Storage |
Cannot store. Verified on UIDAI servers. |
Can store templates locally. |
|
Data Minimization |
UIDAI mandates strict minimization. |
Governed by organizational policy. |
|
Regulatory Authority |
UIDAI and Aadhaar Act 2016 |
DPDP Act 2023 and organizational policy |
|
Compliance Complexity |
High. Strict rules and audit trails. |
Medium. Design within your policies. |
Why Data Minimisation Matters in Aadhaar Systems
Storing more data than required creates exponential compliance and security risks:
Multiple Exposure Points: If you store fingerprints, OTPs, and Aadhaar numbers across your attendance system, employee database, and backup servers, a breach exposes sensitive data from multiple locations.
Audit and Compliance Burden: Each data element stored requires encryption, access controls, audit logs, and retention schedules. More data means more systems to audit.
Regulatory Penalties: UIDAI violations can result in substantial fines and prosecution. Organisations storing prohibited data face legal liability.
The UIDAI framework mandates data minimisation: obtain only what is required, verify identity to achieve your stated purpose, log the attendance event, discard prohibited data, and protect legally stored information.
How Nialabs Ensures UIDAI Compliance in Biometric Attendance
Organisations deploying Aadhaar-based attendance systems must ensure compliance from architecture to implementation. Nialabs provides AI-powered biometric attendance systems designed with UIDAI guidelines built in.
Our attendance management platform separates authentication from data storage. When integrated with Aadhaar, the system captures the attendance event only, ensuring prohibited data is never retained. The system supports both dedicated Aadhaar Data Vaults and general attendance records in separate, secured environments.
For organisations requiring Aadhaar attendance across schools, hospitals, factories, or offices in India, compliance begins with understanding what cannot be stored. From there, system architecture, access controls, and retention policies must enforce those restrictions automatically.
Frequently Asked Questions
Can you store fingerprints captured during Aadhaar authentication in your attendance system?
No. Core biometric data (fingerprints or iris scans) cannot be stored, retained, or archived in any form. The biometric is verified on UIDAI servers; your organisation never receives the actual biometric data. Storing a copy violates UIDAI security mandates and creates legal liability.
What should be done with OTPs sent for Aadhaar authentication?
OTPs must be deleted immediately after authentication. Do not store them in your attendance database, employee records, or audit logs. Even accidental retention through system logs creates compliance violations. Implement log purging to exclude OTPs from permanent archives.
Can Aadhaar numbers be used as employee or student IDs in an attendance system?
No. UIDAI explicitly prohibits using Aadhaar numbers as domain-specific identifiers. If you retain Aadhaar numbers, they must be stored separately in a dedicated Aadhaar Data Vault (ADV) under encryption, not embedded in your general attendance database. Use your own internal employee or student IDs instead.
What is an Aadhaar Data Vault (ADV) and when is it required?
An Aadhaar Data Vault is a separate, secure storage system required by UIDAI 2025 guidelines for organisations that retain Aadhaar numbers. The ADV must use encryption, restricted access, and audit trails. Not all attendance systems need to retain Aadhaar numbers if you use OTP or biometric-only authentication without storing identifiers.
How long can encrypted PID blocks be retained in an Aadhaar attendance system?
A maximum of 24 hours. Encrypted PID (Personal Identity Data) blocks can be cached briefly for buffering during authentication. UIDAI mandates deletion after 24 hours. They cannot be retained as permanent attendance records or audit logs.
What happens if an organization stores prohibited Aadhaar data? What are the penalties?
Violations of UIDAI data storage mandates can result in substantial fines, criminal prosecution, and mandatory deletion of data. Organisations face reputational damage, loss of Aadhaar authentication rights, and civil liability. Compliance is not optional; it is a legal requirement under the Aadhaar Act 2016.
Conclusion: Build Secure, Compliant Aadhaar Attendance Systems
Aadhaar-based attendance offers significant advantages for identity verification and automated attendance marking. However, the convenience comes with mandatory data security obligations under UIDAI guidelines.
The key to compliance is understanding what cannot be stored: biometric data, OTPs, Virtual IDs, and encrypted PID blocks. Aadhaar numbers can be retained only in a dedicated Aadhaar Data Vault under strict access and encryption controls.
A compliant Aadhaar attendance system captures the attendance event only, storing employee or student IDs, names, timestamps, attendance status, and department information. Everything else is discarded.
For schools, colleges, hospitals, offices, and factories deploying Aadhaar attendance across India, audit your current system today. Ensure your architecture, data flow, and retention policies align with UIDAI 2025 guidelines. Non-compliance is not a risk; it is a certainty.